Server-to-server API
Your backend submits a security check and receives the result; enforcement remains in your application.
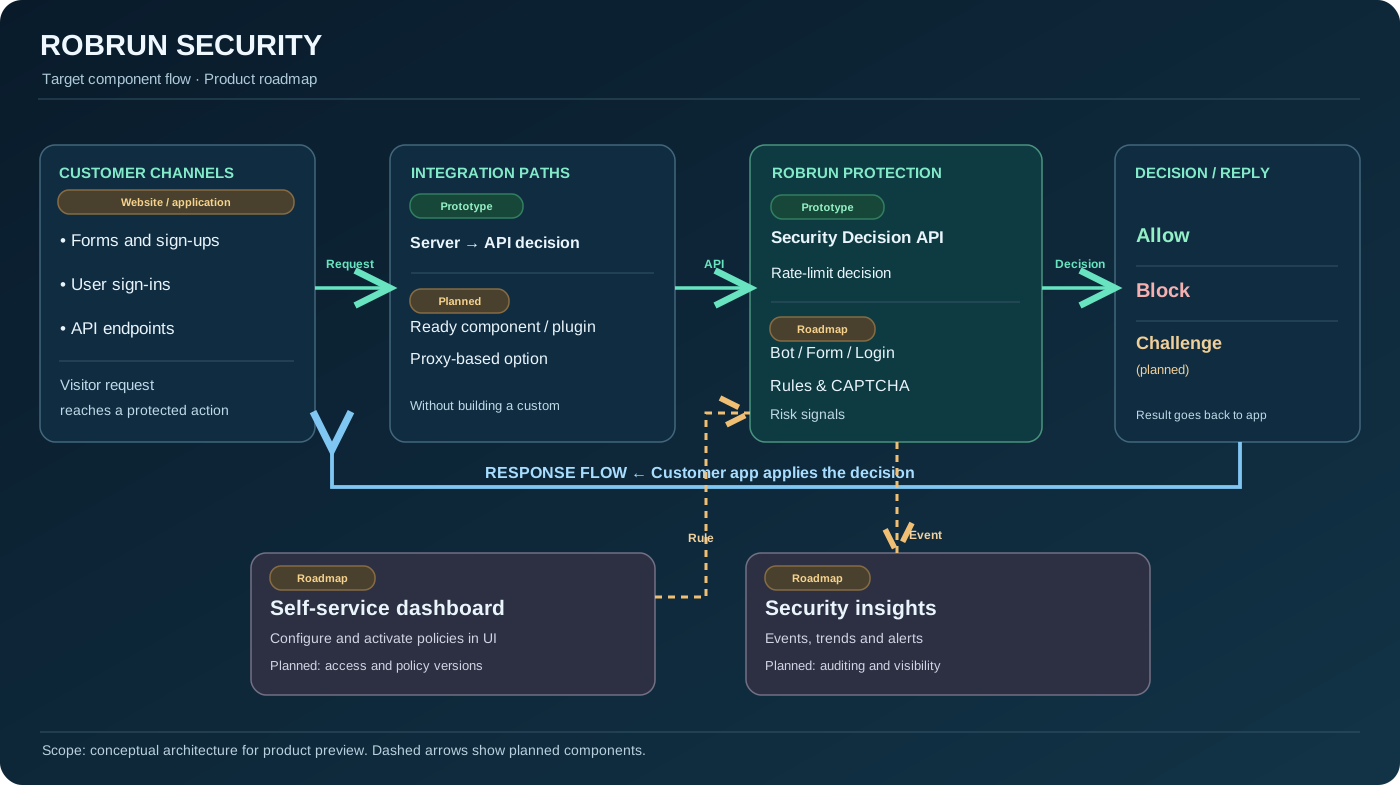
Explore our product vision from incoming requests to security decisions returned to your application. We are building on a tested decision API prototype with planned ready-to-use integrations, CAPTCHA and a self-service dashboard.
The solid green path represents the API prototype; dashed connections indicate planned capabilities. This is a logical target architecture without sensitive infrastructure topology.
Your backend submits a security check and receives the result; enforcement remains in your application.
We are exploring safe installation options such as form components, plugins and suitable proxy integration.
Configure policies in a UI, activate them after integration and review security events in accessible reports.
We use OWASP Top 10:2025, API Security Top 10:2023 and ASVS 5.0.0 to inform requirements and planned assessments. Robrun is not OWASP-certified and is not a full vulnerability scanner.
| Risk area | Planned safeguard / activity | Stage |
|---|---|---|
| Suspicious logins and brute force | Login rate limits; later risk-based verification, related to A07 / API2. | API limit prototype; login defense planned |
| Resource exhaustion and automation | Request limits; future bot signals and controlled blocking, related to API4 / API6. | Fixed-window limits in prototype |
| Form spam and misuse | CAPTCHA with server-side verification, replay prevention and accessible fallback. | In development |
| Access authorization | API-key authentication; separate UI access rules and tests, related to A01 / API1. | API-key prototype; broader review planned |
| Misconfiguration and security logging | Safe defaults, policy review, security-event reporting and alerts, related to A02 / A09. | Planned assessments |
These measures can reduce selected risks; they do not eliminate SQL injection, XSS or all OWASP risks. References: OWASP Top 10, API Security Top 10 and ASVS 5.0.
These are development targets, not verified production capacity or contractual service levels. Peak-load, failover and resilience testing are planned.