Bot protection
Rules for automated traffic and abuse, with no-custom-API setup options on the roadmap.
Bot protection →With or without a custom API, we're developing protection options for bots, spam submissions, suspicious sign-ins and overloaded APIs. Strengthening your security is our mission.
This is a product preview. CAPTCHA, no-custom-API integration and the dashboard are not live customer services yet.
Different services need different integration paths. Explore an area that matters to your business.
Rules for automated traffic and abuse, with no-custom-API setup options on the roadmap.
Bot protection →Challenge workflows designed to reduce spam and unwanted form submissions.
Form security →An additional safeguard against repeated attempts, automated password attacks and suspicious access.
Login security →Tested in development; not yet an openly available commercial service.
Allow/block decisions with reasons and remaining usage limits.
Valkey-backed atomic fixed-window counters by IP and operation, with expiration.
Server-side API key validation and no false approval when the decision backend is unavailable.
We are building intuitive screens so you can manage every policy and activate changes as soon as your integration is complete. The dashboard is not publicly available yet.
Set rules, select protection areas, manage keys and activate changes.
Hosted form components, CMS plugins and reverse-proxy connectors are under evaluation; not yet available.
Show challenges for high-risk actions, with server-side token verification and replay protection.
Attempt limits, temporary restrictions, step-up challenges and false-positive handling.
Understand blocked traffic, trends and key security signals through clear reporting.
HTTPS, key lifecycle, access controls, privacy processes and restore tests.
Sliding windows, token buckets and temporary blocking.
Explainable behavior scoring with adaptive challenges where useful.
PHP/Java examples, safe fallback guidelines and quick integration helpers.
OpenAPI schema validation, inventory and unusual endpoint usage.
Event history, reports, alerts and integrations.
Multi-location failover and measurable reliability. No 99.999% SLA today.
Our roadmap expands the tested API model with ready integrations, UI-managed policies, CAPTCHA and security reporting.
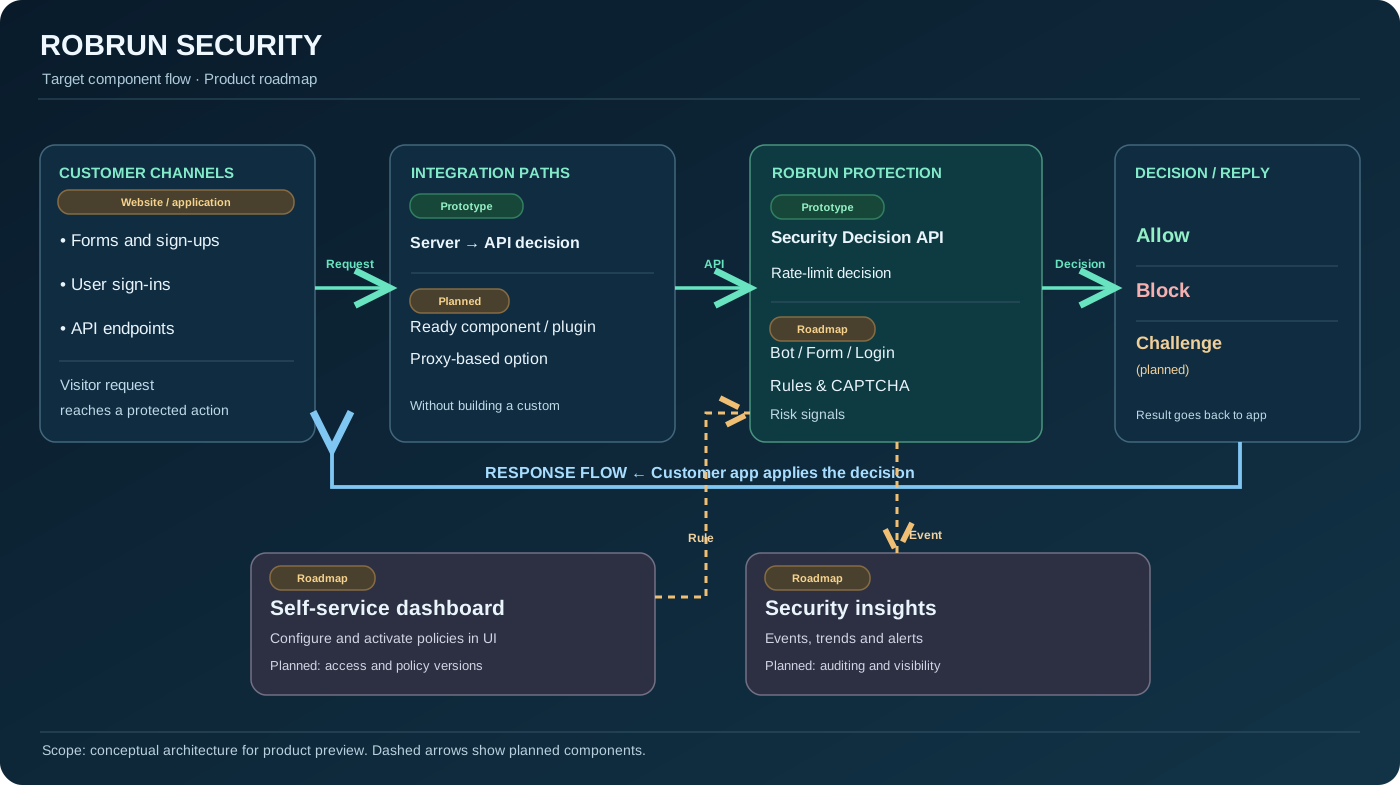 Explore architecture, OWASP-aligned reviews and capacity goals →
Türkiye-based processing and privacy controls, including KVKK-related documentation, remain subject to pre-pilot verification.